
Quick answer
Philippine businesses whose websites collect personal data should map what they collect, write a privacy notice from that map, collect only what is needed, use clear consent wording where consent is the basis, secure forms and hosting, sign agreements with providers, and plan retention, breach response and a named responsible person. This is general information, not legal advice.
- Map every form, booking, newsletter, chat, login, payment page and analytics tool, noting storage, access, outside recipients and retention.
- Place a link to a dated privacy notice beside each submit button and in the footer.
- Check every third-party tool your site sends data to, remove those you do not need and disclose the rest.
If your website collects names, phone numbers, email addresses or any other personal details, Philippine privacy law applies to how you handle them. That covers a simple contact form, a booking page, a newsletter signup and a chat widget.
This guide explains the main duties in plain language and turns them into a checklist you can use for your website. It is practical guidance, not legal advice.
This is general information, not legal advice. Check your situation with a qualified adviser.
The law in brief
The Data Privacy Act of 2012 (Republic Act 10173) protects personal information, and the National Privacy Commission (NPC) administers it. Its Implementing Rules and Regulations set the detailed duties. The law is built on a few principles that matter for a website: be open about what you collect and why (transparency), collect for a clear and legitimate purpose, and collect only what is needed for that purpose (proportionality).
If you decide why and how personal data is collected, you are generally a “personal information controller”. Providers that handle data for you, such as a hosting company or an email tool, are “processors”. You stay accountable for what your processors do on your behalf.
Step 1: map the data your website collects
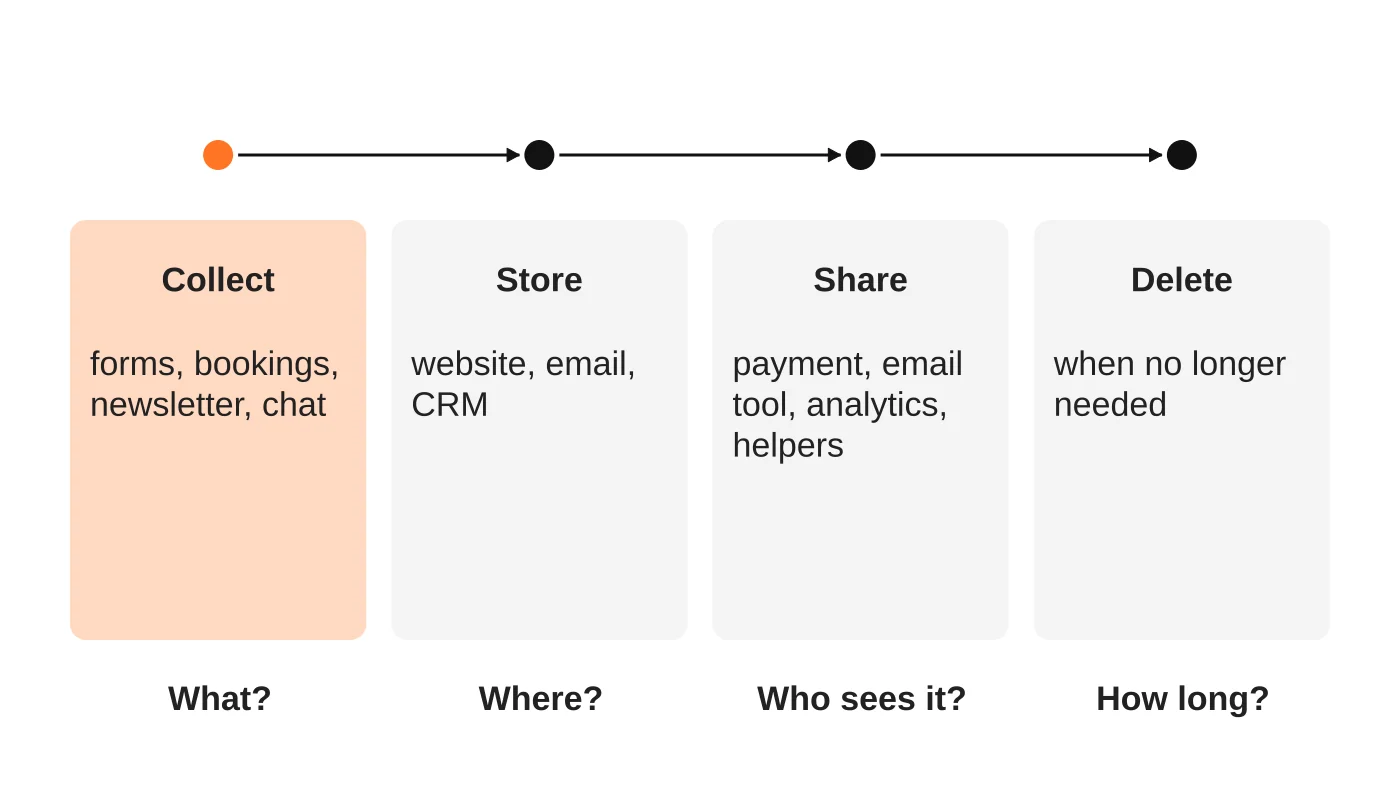
Before writing a notice, list every place your site collects data. Include forms, bookings, newsletters, live chat, comments, login accounts, payment pages and analytics. For each one, note what you collect, where it is stored, who can see it, which outside services receive it and how long you keep it. You cannot write an honest privacy notice without this list.
Choosing where to host? Compare Philippine and overseas hosting for speed, data location and support.
Step 2: write a clear privacy notice
A privacy notice explains your data handling to the people whose data you collect. Commentary from privacy practitioners notes that a proper notice answers questions such as who is in control of the processing, what personal data is collected, why and how it is used, who it is shared with, how long it is kept and how people can exercise their rights. Write it after you have mapped your actual practices, not from a copied template.
The NPC’s own website notice is a useful example: it states plainly that the site uses a third-party service to analyse web traffic and that the service uses cookies.
Place a link to the notice wherever you collect data, next to each form submit button and in the footer. Date it and keep earlier versions.
The checklist
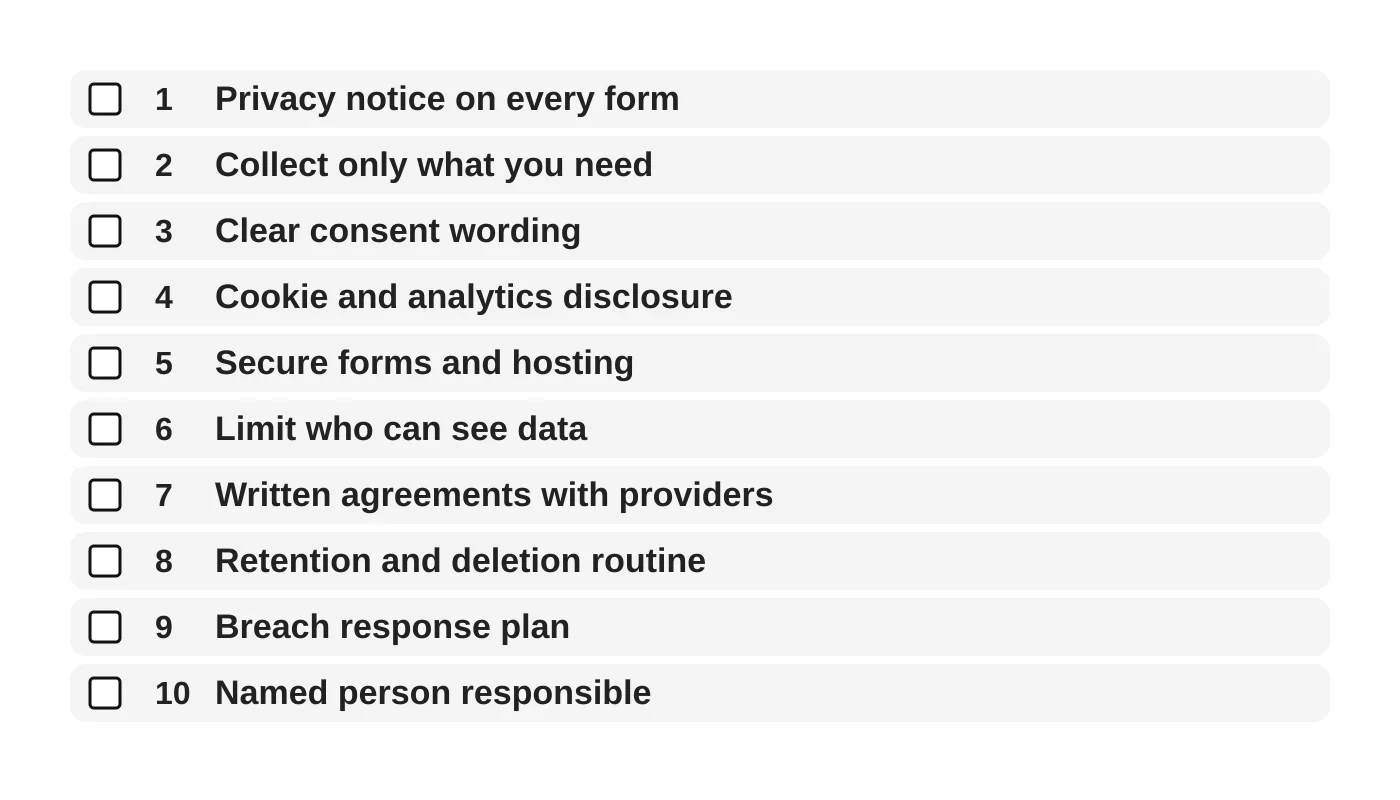
- Privacy notice on every form. A short sentence and a link at the point of collection.
- Collect only what you need. Does a contact form really need a date of birth?
- Clear consent wording where consent is your basis. Use plain language, avoid pre-ticked boxes and describe each purpose.
- Cookie and analytics disclosure. Say which tools set cookies, why and how people can opt out where you offer that.
- Secure forms and hosting. Use HTTPS, keep software updated and protect admin logins. See the five layers of website security.
- Limit who can see data. Give staff and assistants the minimum access they need. See the offboarding checklist.
- Written agreements with providers that handle data for you, covering security and what happens to data at the end of the contract.
- A retention and deletion routine. Delete old enquiries and exports you no longer need.
- A breach response plan. Know who decides, who is told and how you will assess impact. See what a website breach costs.
- A named person responsible. Many organisations must designate a data protection officer.
Registration and notification duties
The NPC runs an online registration system, the NPC Registration System, launched on 3 February 2023, through which controllers and processors register data processing systems and their data protection officers under NPC Circular 2022-04. Whether and when your organisation must register depends on factors set in the rules, so check the current text or ask your adviser rather than assuming either way.
If a breach involves personal data that could cause serious harm, notification duties apply, and the NPC’s breach rules set strict timelines. The details are in the NPC’s breach circular.
Third parties your website uses
Most websites send data to other companies without anyone noticing: analytics, fonts, embedded videos, chat tools, payment gateways, email platforms and advertising pixels. Check each one. Remove tools you do not need, and disclose the ones you keep in your notice. Keep a short register of tools and who approved them.
Working with offshore teams and AI tools
If a virtual assistant or an offshore developer can see customer data, they are part of your data handling. Give them access only through your accounts, with written confidentiality terms, and train them on the rules. For AI tools, set clear limits on what may be pasted into them. The one-page AI use policy gives a template, and managed or self-managed offshore teams covers who is accountable for what.
Before reposting anything a customer made, follow this customer photo and user-generated content permission workflow.
Frequently asked questions
Does a small business need a privacy notice?
If your website collects personal data, yes. A short, honest notice is better than none.
Do we need cookie banners?
The law does not use that word, but transparency does apply to tracking tools. At a minimum, disclose what you use and why. Check with your adviser about consent for non-essential tracking.
Who is responsible if our hosting provider is breached?
You remain accountable as the controller, while the provider has its own duties. Choose providers carefully and keep written terms.
Can we keep every enquiry forever?
No. Keep personal data only as long as needed for the purpose, and delete or anonymise it afterwards.
Where should we start?
Start with the data map. Everything else follows from it.
Make your website privacy-ready
Web Design Davao’s web design and development team can add privacy notices, consent wording and secure forms to your site. We recommend a lawyer review your notice. Ask about a privacy review.


